Cost-Effective Cloud Security and Optimization: Doing More With Less
The conventional wisdom is that security costs money and optimization saves it - therefore they're in tension. In practice, a well-designed cloud security and optimization program does both simultaneously, often using the same underlying data and tooling.
This guide is for engineering leaders who need to improve security posture and reduce cloud spend without doubling their tooling budget or headcount.
Why Security and Cost Are Connected
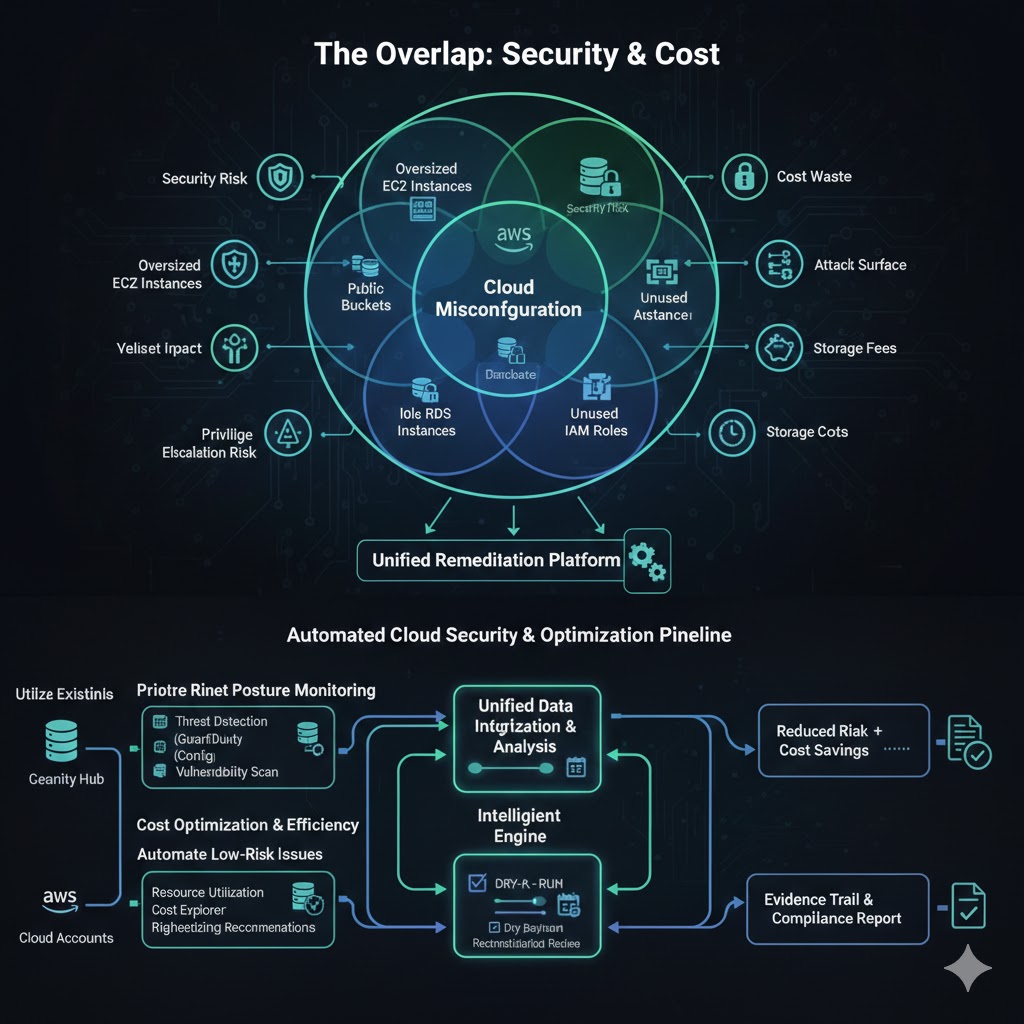
Cloud misconfigurations drive both security risk and cost waste. An oversized EC2 instance running at 3% CPU is wasting money. If it also has a permissive security group with port 22 open to 0.0.0.0/0, it's also a security risk. Fixing the security misconfiguration and right-sizing the instance are both optimization actions on the same resource.
Similarly, unused resources - orphaned EBS volumes, forgotten Elastic IPs, idle RDS instances - represent both wasted spend and unnecessary attack surface. Cleaning them up improves your financial position and reduces the area attackers can exploit.
The Overlap Diagram
| Resource Issue | Security Impact | Cost Impact |
|---|---|---|
| Oversized EC2 instances | Larger blast radius if compromised | Paying for idle capacity |
| Public S3 buckets | Data exposure risk | Potential egress charges |
| Idle RDS instances | Unnecessary attack surface | Full instance cost while idle |
| Old EC2 snapshots | Outdated data retention risk | Storage costs accumulate |
| Unused IAM roles with broad permissions | Privilege escalation risk | None directly, but breach costs are high |
| Unencrypted storage | Compliance violation risk | None directly |
Building a Cost-Effective Program
Start With What You Have
Before buying more tools, fully utilize what you're already paying for. AWS provides significant security capabilities natively:
- AWS Config: Configuration compliance monitoring
- GuardDuty: Threat detection
- Security Hub: Centralized finding aggregation
- Cost Explorer: Spend analysis
- Trusted Advisor: Basic cost and security recommendations
Many organizations pay for these services but don't act on their findings. Closing the remediation gap on native tool findings alone can meaningfully improve your posture.
Consolidate Overlapping Tools
Security tool sprawl is expensive and creates integration overhead. Evaluate your current toolchain for overlap. Do you have three tools that all detect public S3 buckets? Are you paying for a CSPM tool and a separate cost management tool when a platform like Dedups.ai provides both?
Prioritize High-Impact Remediations
Not all findings are equal. A scoring model that weighs security impact against cost impact against remediation effort helps teams work on what matters most. A finding that saves $2,000/month in cloud spend and removes a critical security misconfiguration is worth addressing before one that saves $50 and represents a low-severity configuration issue.
Automate Remediation for Low-Risk Issues
Some security and cost remediations are low-risk enough to automate: deleting unattached EBS volumes older than 90 days, disabling public access on S3 buckets with no legitimate public traffic, removing unused Elastic IPs.
Dedups.ai supports this through scheduled remediations with dry-run previews - you see what will change before it changes, can verify the blast radius, and then schedule the fix for a comfortable maintenance window.
The Evidence Trail Problem
Here's a cost optimization consideration that teams often miss: compliance audits are expensive. Pulling together evidence that your security controls are working costs engineering time and frequently disrupts normal operations.
A platform that automatically collects remediation evidence - who approved it, what changed, when it ran, what the before and after state was - dramatically reduces audit preparation costs. Dedups.ai generates this evidence trail automatically for every remediation, mapping findings to ISO 27001 and SOC 2 controls.
Measuring ROI on Security and Optimization Spend
For each tool or initiative, track:
- Direct cost savings: Reduced AWS spend from optimization actions
- Risk reduction value: Estimated cost of incidents prevented (harder to measure but real)
- Engineering time saved: Hours saved through automation vs. manual remediation
- Compliance cost reduction: Reduced audit preparation time
Dedups.ai tracks realized savings for every completed optimization recommendation, giving you a measurable ROI number you can bring to leadership discussions.
Ready to Get Started?
Security and cost optimization don't have to compete for budget. Dedups.ai provides a unified platform that addresses both simultaneously - continuous security posture monitoring, AI-powered cost optimization, and automated remediation with full evidence collection. Start your free assessment and see your optimization opportunities today.