AWS Security Tools: Building a Complete Toolchain Without the Chaos
AWS security tools span dozens of categories from identity management to threat detection, vulnerability scanning, compliance monitoring, and incident response. Most organizations accumulate tools over time - adding one when a new requirement appears, another when an auditor asks for it - until they have a collection of overlapping, poorly-integrated tools that costs more to maintain than it delivers in security value.
Building a coherent AWS security toolchain means thinking about coverage, integration, and total cost of operation - not just individual tool capabilities.
The AWS Security Coverage Map
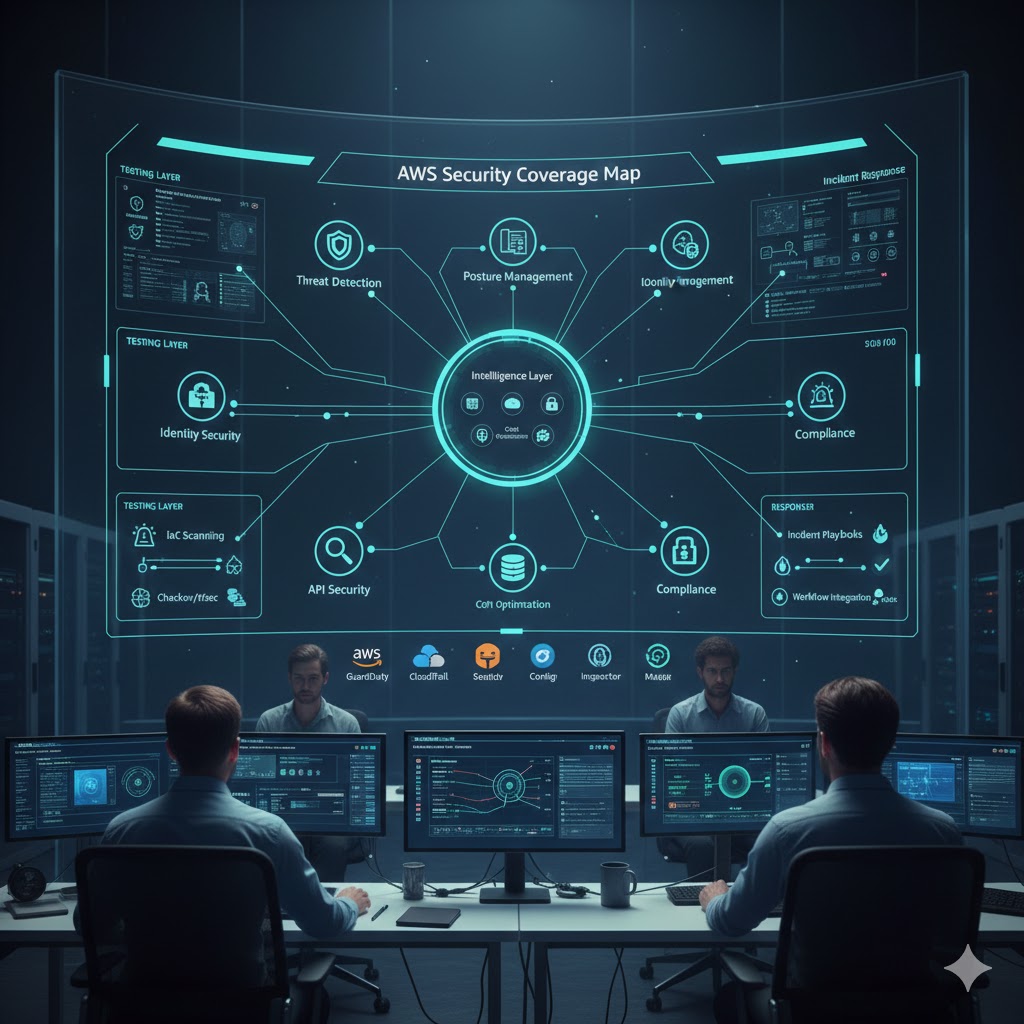
A complete AWS security program needs coverage across these domains:
| Domain | Required Capability | Recommended Approach |
|---|---|---|
| Threat detection | Identify active attacks and compromises | GuardDuty + SIEM |
| Posture management | Find and fix misconfigurations | Dedups.ai (CSPM) |
| Vulnerability management | Find unpatched CVEs in workloads | Amazon Inspector + Dedups.ai |
| Identity security | Manage IAM risk | IAM Access Analyzer + Dedups.ai |
| Data security | Protect sensitive data | Macie + encryption enforcement |
| API security | Discover and test APIs | Dedups.ai |
| Network security | Control traffic and detect anomalies | GuardDuty + VPC Flow Logs |
| Incident response | Contain and investigate incidents | CloudTrail + IR runbooks |
| Compliance | Demonstrate control effectiveness | Security Hub + Dedups.ai |
Avoiding Tool Sprawl
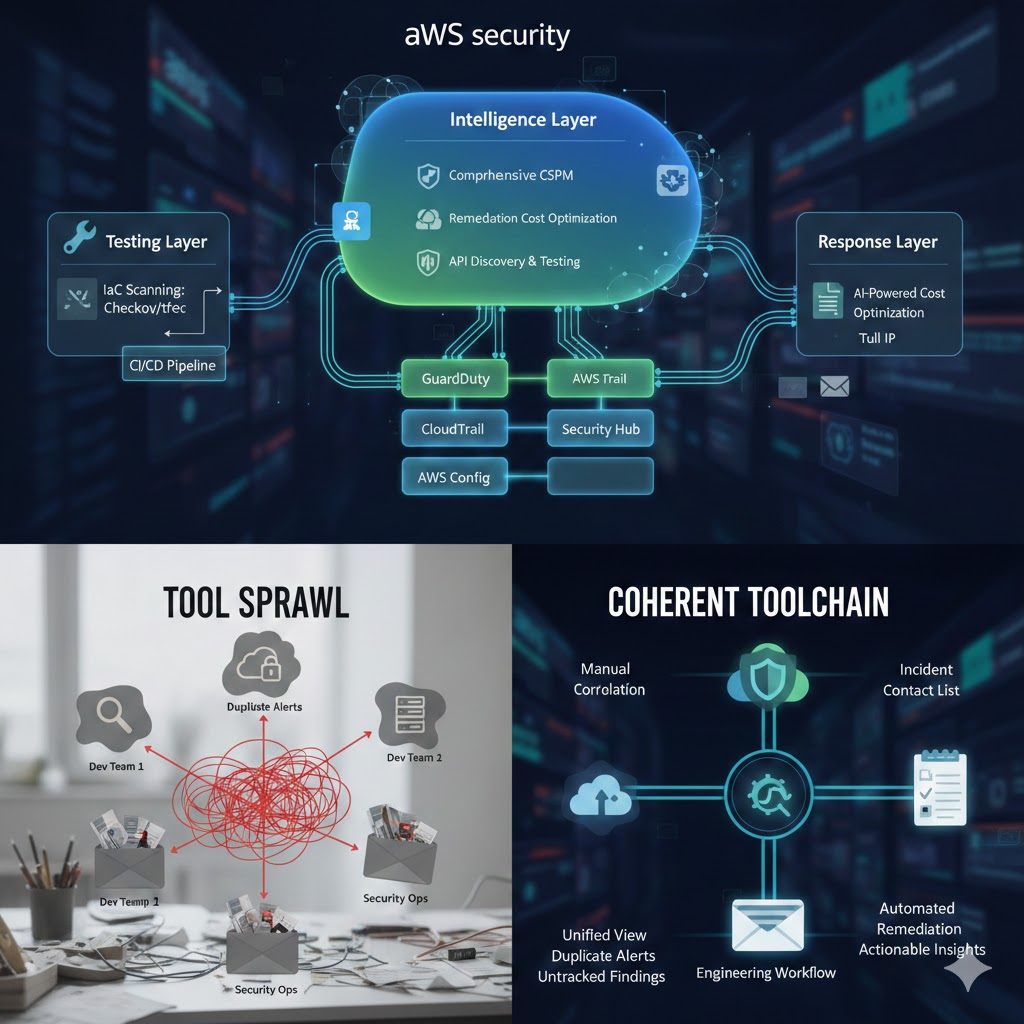
Tool sprawl is the #1 operational risk in cloud security programs. Signs of tool sprawl:
- Multiple tools scanning the same AWS accounts for overlapping findings
- Engineering teams receiving security alerts from three different systems
- Security findings that live in tool dashboards nobody monitors
- Quarterly audits that require manually aggregating evidence from five different tools
The solution isn't buying fewer tools - it's buying tools that are designed to work together and consolidating overlapping capabilities.
Building the Toolchain
Foundation Layer: AWS Native Tools
Start with what AWS provides. These are already paid for as part of your AWS usage and provide solid foundational capabilities:
- GuardDuty: Enable in all accounts, all regions. Non-negotiable.
- CloudTrail: Enable in all accounts, all regions with log file validation.
- AWS Config: Enable with a core set of managed rules aligned to your compliance framework.
- Security Hub: Enable to aggregate findings from native services.
This foundation costs roughly $50–500/month depending on environment size and is the baseline every AWS security program should have.
Intelligence Layer: Third-Party CSPM
AWS native tools don't provide misconfiguration remediation workflow, cost optimization, or API security. This is where a third-party platform like Dedups.ai fills the gaps.
| Capability | AWS Native | Dedups.ai |
|---|---|---|
| Misconfiguration detection | AWS Config rules | Comprehensive CSPM |
| Remediation workflow | None | Jira/Slack/email integration |
| Cost optimization | Trusted Advisor (basic) | AI-powered recommendations |
| API security | None | Discovery + testing |
| IP vulnerability scanning | Inspector (EC2 only) | Full external scan |
| Compliance evidence | Manual | Automated |
Testing Layer: Pre-Deployment Security
For teams using Infrastructure as Code, add IaC scanning to catch security issues before they reach production:
- Checkov or tfsec: Open-source IaC scanners for Terraform and CloudFormation
- Integrate into your CI/CD pipeline as a blocking check
Response Layer: Incident Handling
- Document IR runbooks for your top 5 incident scenarios
- Maintain an incident response contact list
- Consider an IR retainer with a managed security provider for serious incidents
Integration Is the Differentiator
A toolchain where each tool sends findings to a separate place - GuardDuty to Security Hub, CSPM findings to a portal, cost alerts to email - requires engineers to monitor multiple channels and manually correlate findings. This is inefficient and leads to missed issues.
Dedups.ai addresses this by routing all findings through your engineering workflow tools (Slack, Jira, email), with context that enables action without additional research. Engineers see security and cost findings for resources they own, in the tools they already use.
Ready to Get Started?
Building a coherent AWS security toolchain is more about integration and workflow than tool count. Dedups.ai provides the CSPM, cost optimization, API security, and IP scanning layers in a single platform - connecting to your existing AWS environment and engineering workflow tools without requiring extensive configuration or dedicated security staff.