AWS Security Services: Native Tools vs. What You Still Need
AWS ships an impressive suite of native security services. GuardDuty, Security Hub, Macie, Inspector, Config - each solving a real security problem within the AWS ecosystem. But AWS's native services have gaps, and understanding those gaps is essential for building a complete cloud security program.
This guide maps AWS native security services against what they cover, what they miss, and what you need alongside them.
AWS Native Security Services: A Practical Map
| AWS Service | What It Does Well | Key Limitation |
|---|---|---|
| AWS Config | Tracks configuration changes, compliance rules | Limited remediation support, no workflow integration |
| Amazon GuardDuty | Threat detection from CloudTrail/DNS/VPC Flow Logs | No misconfiguration detection |
| AWS Security Hub | Aggregates findings from multiple sources | Still requires manual triage and routing |
| Amazon Macie | Sensitive data discovery in S3 | S3 only, no broader data classification |
| Amazon Inspector | Vulnerability scanning for EC2 and containers | Limited to compute, no cloud-level misconfigs |
| AWS IAM Access Analyzer | Identifies overly-permissive resource policies | IAM and resource policies only |
| CloudTrail | API activity logging | Analysis and threat detection requires additional tooling |
| AWS WAF | Web application firewall | Requires careful rule configuration, no API discovery |
What AWS Native Services Do Well
GuardDuty: Excellent Threat Detection
GuardDuty is one of AWS's best security investments. It analyzes CloudTrail logs, DNS queries, and VPC Flow Logs using threat intelligence to detect:
- Unusual API call patterns that may indicate compromised credentials
- Communication with known malicious IP addresses
- Cryptocurrency mining activity
- S3 anomalous access patterns
At $0.55–$4 per million events (depending on data source), it's cost-effective for the detection capability it provides. Enable it in every account, in every region. There's no reason not to.
AWS Config: Solid Compliance Foundation
Config maintains a timeline of resource configuration changes and supports custom compliance rules via AWS Config Rules (including a large library of managed rules). For organizations building around CIS AWS Benchmark compliance, Config rules provide a native implementation of many required checks.
The limitation is that Config rules tell you when something is non-compliant - they don't help you fix it or route the finding to the right engineer.
Security Hub: Good Aggregation, Weak Remediation
Security Hub aggregates findings from GuardDuty, Inspector, Macie, Config, and third-party tools into a single view. This is genuinely useful for large security teams running a dedicated SOC operation.
For smaller teams, Security Hub findings without a downstream remediation workflow still pile up without getting addressed. The findings are accurate - the workflow is missing.
What AWS Native Services Don't Do
Misconfiguration remediation workflow: AWS native services detect issues but provide no structured workflow to route findings to the responsible engineer, track remediation status, or collect evidence that the fix was applied.
Cross-domain correlation: An EC2 instance with a permissive security group (security finding) that's also oversized and idle (cost finding) appears as separate signals in AWS tools. An integrated platform like Dedups.ai surfaces these as a single resource issue.
Cost optimization: AWS Cost Explorer and Trusted Advisor provide basic cost optimization guidance, but lack the ML-driven recommendations, workflow integration, and evidence tracking of a dedicated platform.
API security: AWS doesn't provide comprehensive API discovery and security testing. Third-party tools are required.
IP vulnerability scanning: AWS Inspector scans EC2 instances for known CVEs. External attack surface scanning requires separate tooling.
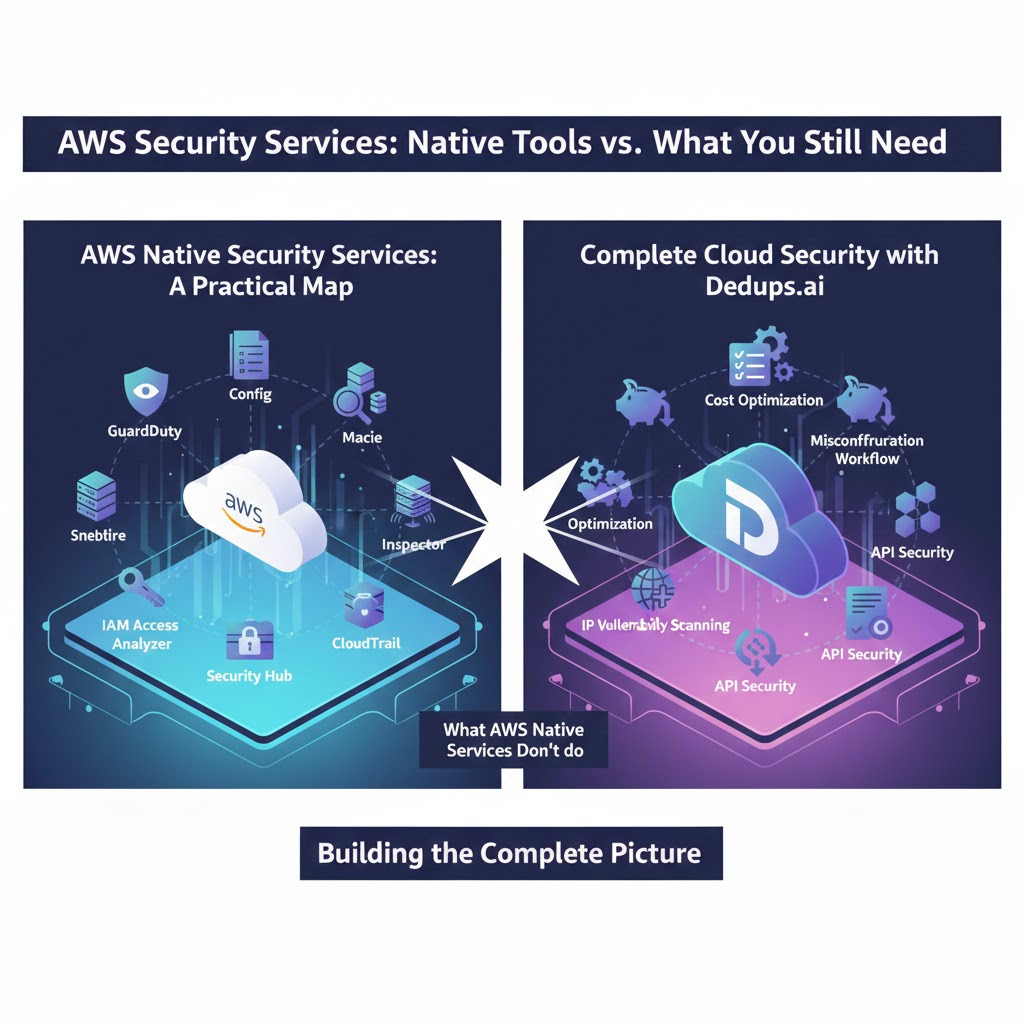
Building the Complete Picture
A practical AWS security program combines native services with third-party tooling:
Use AWS native services for: Threat detection (GuardDuty), log collection (CloudTrail), data discovery (Macie), configuration history (Config)
Supplement with Dedups.ai for: Misconfiguration detection with remediation workflow, cost optimization, API security, IP vulnerability scanning, compliance evidence generation, and engineering-workflow integration
Ready to Get Started?
AWS native security services are a strong foundation - but they're not a complete security program. Dedups.ai fills the critical gaps in the AWS native security stack, particularly around misconfiguration remediation, cost optimization, and API security. Start your free assessment to see exactly what your native tools are missing.